Evaste
KVKK/GDPR Cookie Consent Management Platform
Overview
Evaste is a consent management platform (CMP) built at Group Taiga that lets any website meet KVKK and GDPR obligations for cookies and third-party tracking. It spans three tightly integrated pieces I designed and built end to end: an embeddable vanilla-JS consent widget that runs on customer sites, a React admin dashboard where businesses configure domains and banners, and a .NET microservices backend that logs consent, aggregates analytics and handles billing. The product is engineered around a core principle: no tracker fires until the visitor has actually consented.
What It Does
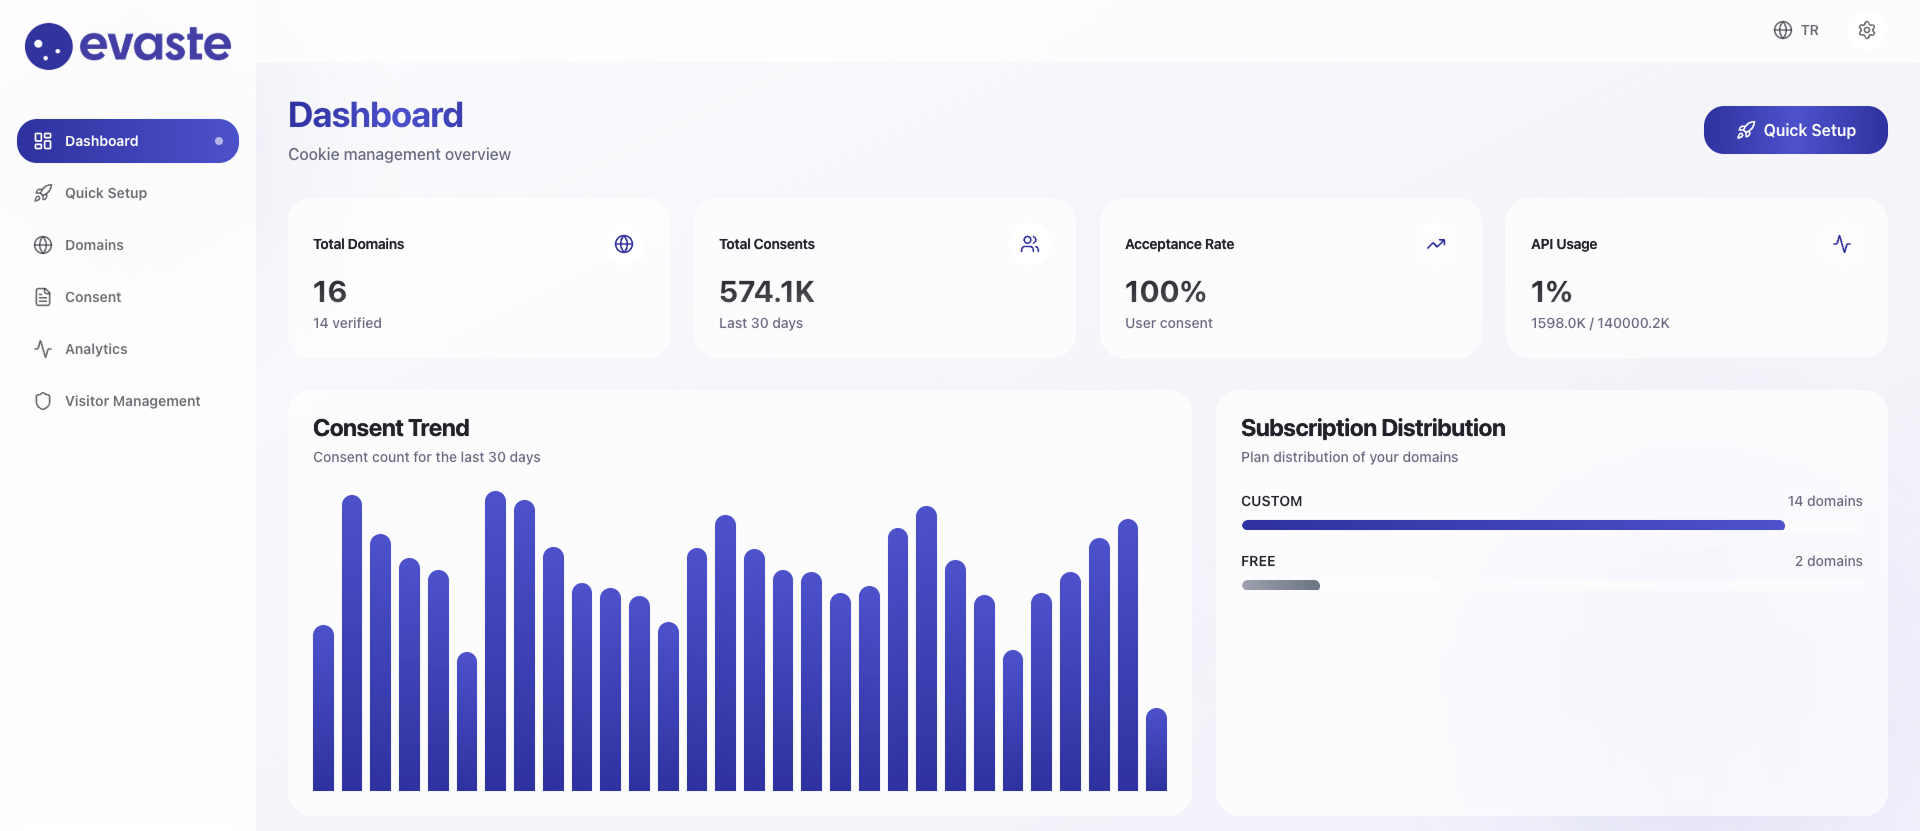
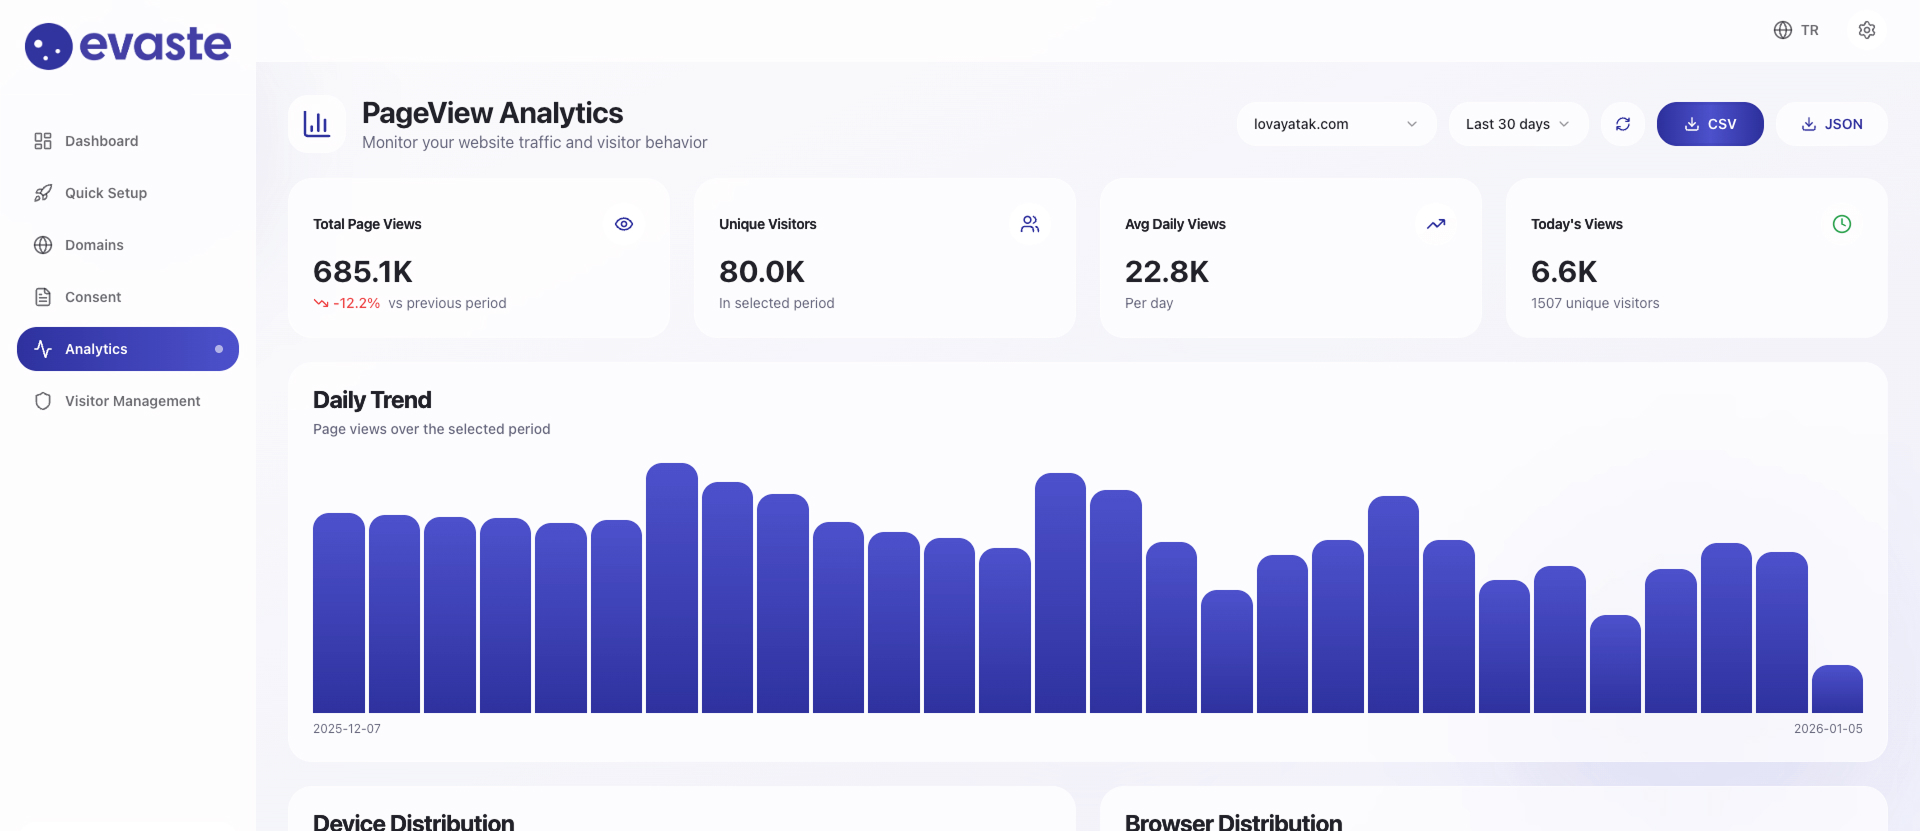
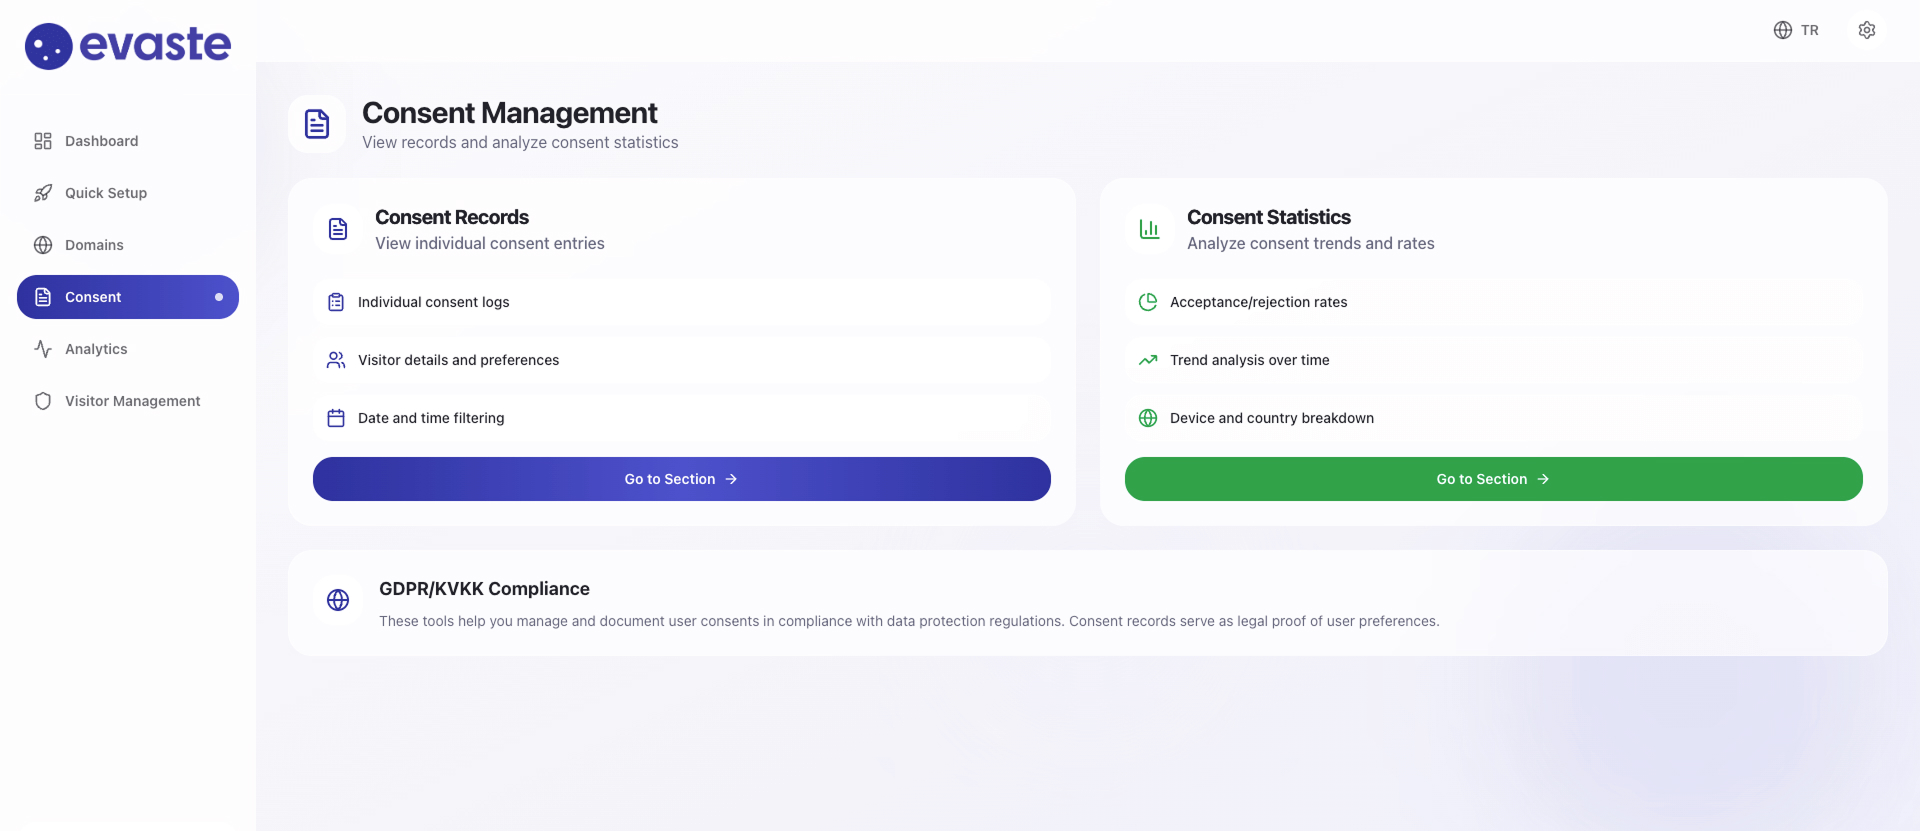
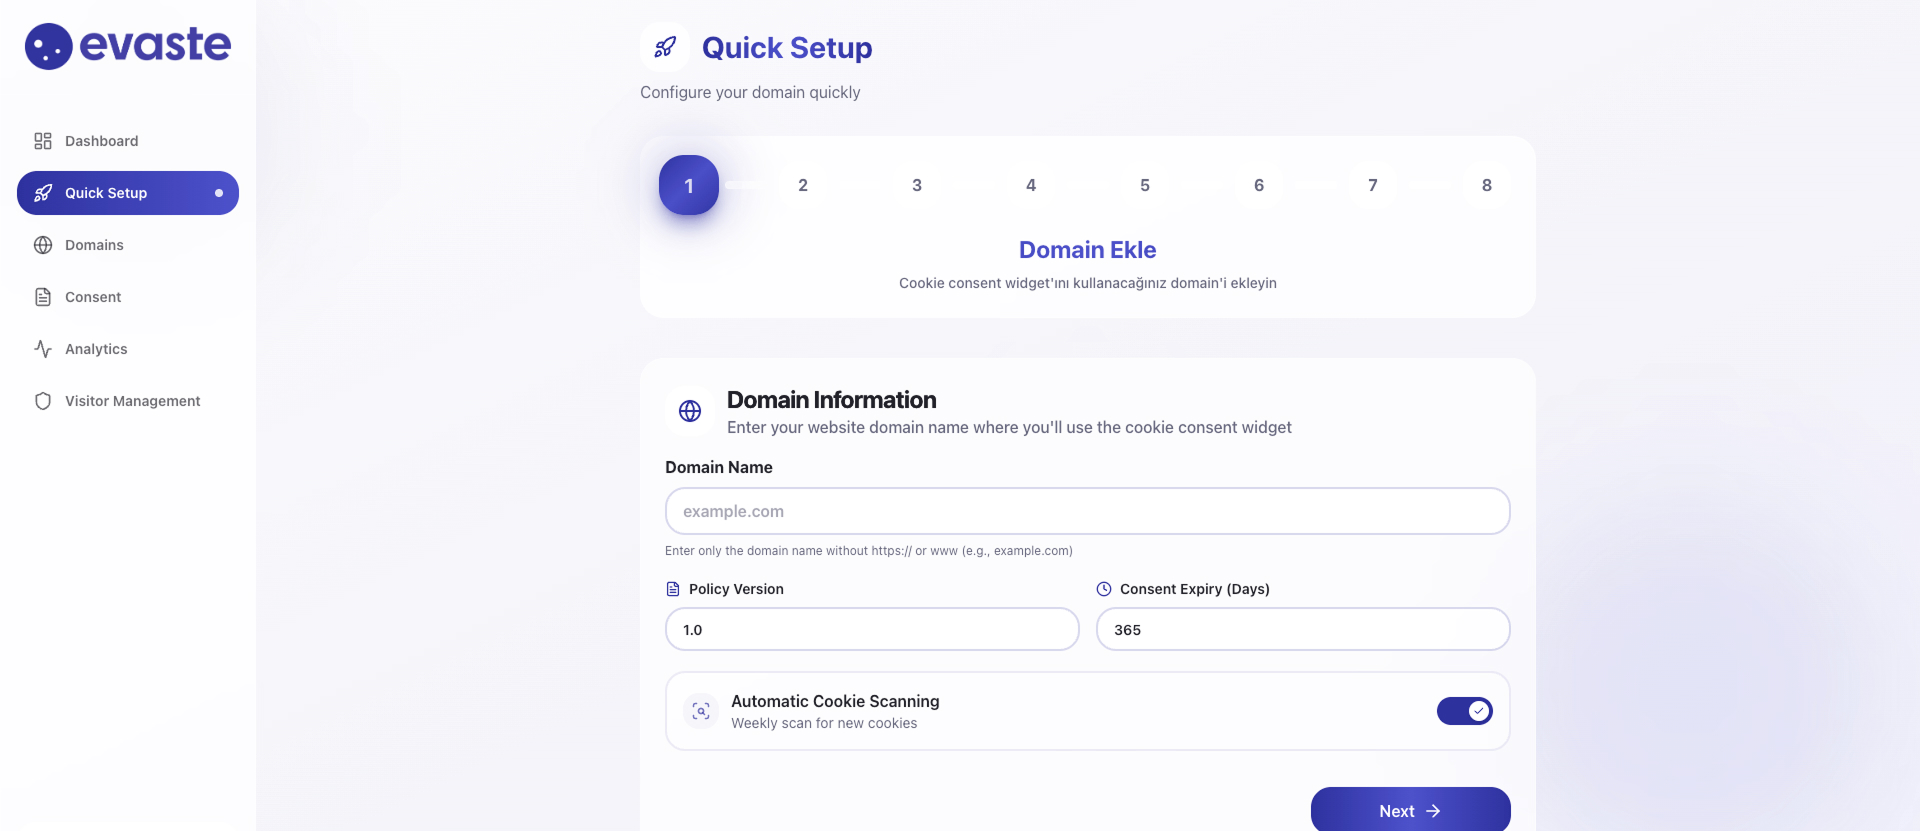
On a customer site, a lightweight script blocks known tracking scripts before they can execute, shows a compliant consent banner, and unblocks each category only after the visitor opts in, while wiring straight into Google Consent Mode v2 and GTM. In the dashboard, businesses add domains, run an automated cookie scan, customize the banner's appearance, behavior and multi-language content with a live preview, and review consent records, statistics and pageview analytics. Behind the scenes the backend records every consent decision with a legal audit trail, aggregates privacy-preserving pageview data for billing, and manages subscriptions.
Tech Stack
Key Features
Embeddable vanilla-JS widget that blocks tracking scripts pre-consent via createElement interception and MutationObservers, then recreates them on opt-in
Google Consent Mode v2 (seven signals, default-denied) plus dataLayer/GTM events, with direct consent bridges for Microsoft Clarity, Meta Pixel, TikTok and others
Domain-keyed blocklist mapping ~90 tracking hostnames to consent categories (Necessary, Analytics, Marketing, Functional, Social)
Playwright-based cookie scanner that scrolls, auto-accepts existing banners, detects cookies with wildcard patterns and enriches them from external cookie databases
React admin dashboard for domain onboarding, banner appearance/behavior/content customization with live preview, and a 13-language content editor
Separate Analytics microservice with its own database and hierarchical pageview rollups (raw to hourly, daily and monthly)
Privacy-first tracking: salted SHA-256 IP hashing without consent, AES-encrypted raw IP only with consent, plus bot-detection middleware for accurate billing
GDPR compliance engineering: per-consent text snapshots, consent change-history audit trail, and visitor data erasure and export endpoints
iyzico subscription billing with card tokenization, 3D-Secure and automated saved-card renewals across tiered plans
Gallery
Technical Highlights
Key Achievements
Built a full three-tier CMP single-handedly: embeddable SDK, React dashboard and .NET microservices backend
Engineered a robust pre-consent script-blocking layer (createElement override plus dual MutationObservers) that keeps trackers dormant until opt-in
Architected a fully independent Analytics microservice with its own database and RabbitMQ-driven ingestion
Implemented Redis distributed locking to guarantee single-execution scheduled jobs across horizontally scaled workers
Delivered deep Google Consent Mode v2 / GTM integration and per-platform consent bridges for major ad and analytics tools
Automated compliance operations with a Playwright cookie scanner and a weekly re-scan worker that notifies owners of newly detected cookies
Impact & Results
Gave Group Taiga a production CMP that lets customer websites stay KVKK/GDPR-compliant without blocking trackers ahead of consent or hand-maintaining cookie inventories. The microservices design, RabbitMQ pipeline and Redis-coordinated workers let consent logging and analytics scale horizontally on Kubernetes, while salted hashing, encryption and audit trails keep the platform itself privacy-compliant by construction.